Company: Security & Trust
Security you can verify
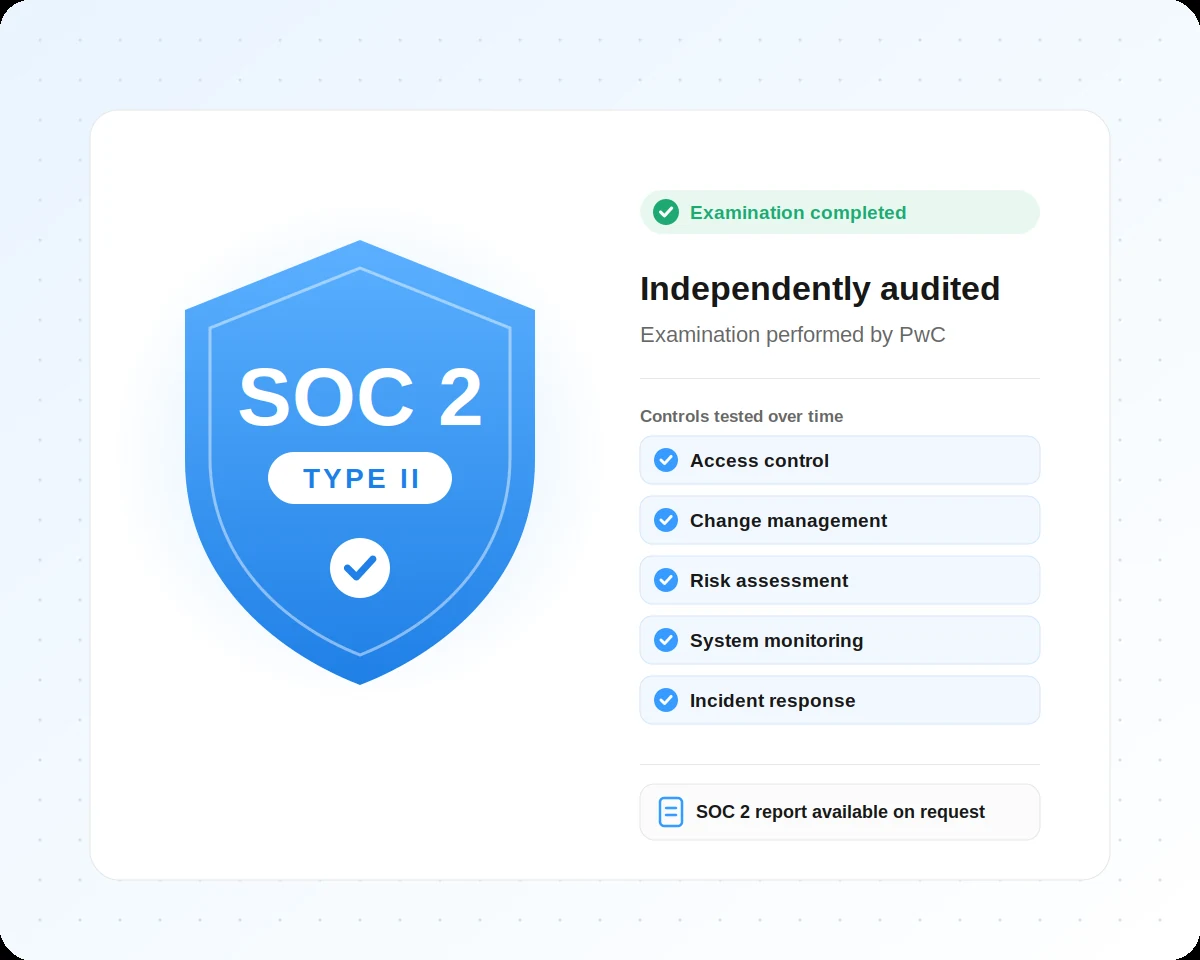
Nominis is SOC 2 Type II attested, following an independent examination by PwC. The examination assessed whether our security controls are suitably designed and operate effectively over time, so you can trust how we protect your data and your investigations.
What SOC 2 Type II means
SOC 2 is an auditing framework created by the AICPA to evaluate how service organizations protect customer data, measured against its Trust Services Criteria. A Type I report checks whether controls are designed correctly at a single point in time. A Type II report goes further: the auditor tests whether those controls actually worked, consistently, across an extended observation period.
Why it matters to our customers
Independent assurance
Our controls were examined by PwC, an independent auditor, rather than self-assessed. You get a third-party view of how we operate.
Tested in practice, not just on paper
Type II means our controls were tested over a period of time, covering areas such as access control, change management, risk assessment and monitoring.
Faster vendor due diligence
Security and compliance teams can rely on our SOC 2 report to speed up vendor risk reviews, onboarding and procurement.
Frequently asked questions
What is a SOC 2 Type II report?
It is an independent auditor's report on how a service organization protects customer data. Unlike a Type I report, which looks at control design at a single point in time, a Type II report tests whether those controls operated effectively over an observation period.
Who performed the Nominis SOC 2 examination?
The Nominis SOC 2 Type II examination was performed by PwC.
How can I get a copy of the SOC 2 report?
Contact our team and we will share the report with you. SOC 2 reports are typically shared under a non-disclosure agreement.
Is SOC 2 a certification?
Not exactly. SOC 2 is an attestation: an independent auditor issues a report with an opinion on a company's controls, rather than a certificate. It is the standard way software providers demonstrate their security practices to customers.